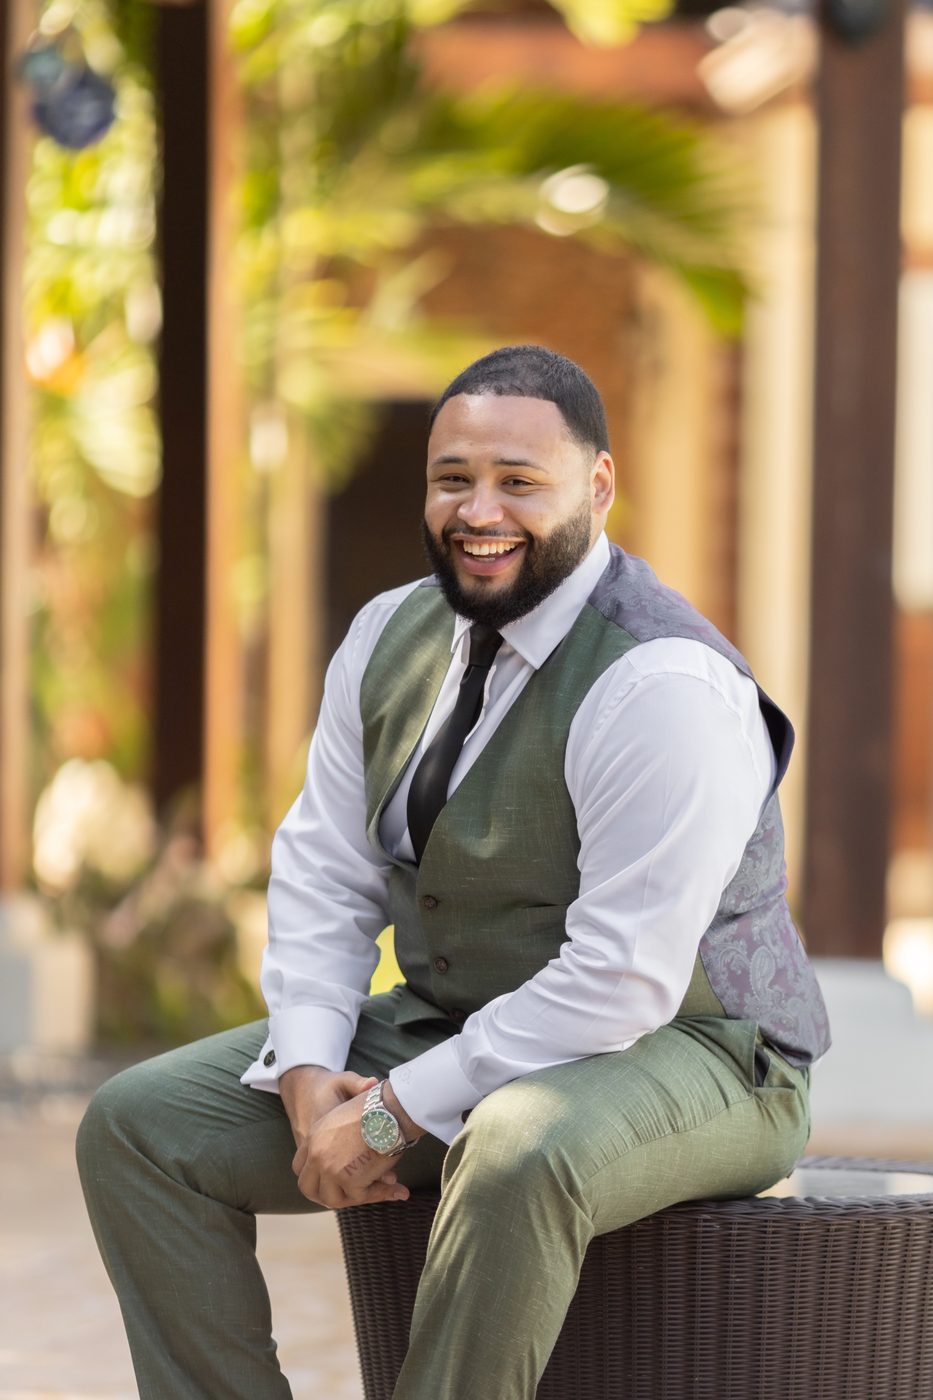
Ashland, MA · Greater Boston · Open to director-level roles

Roger Figuereo

IT & Security LeaderInfrastructure, Security Operations & AI Governance

Fifteen years owning enterprise IT and security end to end — a decade running a $1.7M function with a team of three, today a $1.1M+ technology portfolio and a production agentic AI governance program in a business that had none.

  • CISSP
  • Security+
  • U.S. Army veteran
  • Clearance-eligible
  • English / Spanish
Roger Figuereo

Scope ledger

Job titles at small technology organizations rarely track accountability. This is the honest accounting of the function I currently run — the same one a hiring committee would inherit.

Title of record

Senior Systems & Security Administrator

NOBULL — national consumer brand, ~200 employees. May 2025 to present.

Actual mandate

Owner of the enterprise security and systems function

Senior IT and security owner for a ~200-employee national DTC athletic brand. One direct report, a $1.1M+ annual technology budget across 15 vendor contracts, and the full security and AI governance stack.

Nine domains · one function

Selected work

Programs I built and ran.

Governance — NOBULL

An agentic AI program governed before it shipped

Leadership wanted AI capability across the company. I built the control structure first — the AI Acceptable Use Policy and an MCP Permission Policy governing a 17-permission delegated access model, mapped to NIST AI RMF 1.0 and ISO/IEC 42001 — took it through executive approval, then matched the tooling to the work rather than standardizing on one vendor: ChatGPT and Microsoft Copilot for the whole office, Claude for power users and code, Perplexity for research and market analysis.

Four enterprise AI platforms in production under written policy, each matched to a real need rather than accumulated by department demand.

Brand protection — NOBULL

A hundred counterfeit storefronts taken down

Customer-facing commerce properties were exposed at the edge and the brand was being counterfeited at scale. I run the takedown program against storefronts trading on the name, and architected the WAF and DDoS protection standing behind it.

100+ counterfeit storefronts removed. The perimeter absorbed 60 DDoS attacks over 12 months and now turns away 46% of inbound traffic as malicious, roughly 72.7M bot requests a month.

Compliance — Elkus Manfredi Architects

Taking a 300-person firm through certification

I led the firm to ISO/IEC 27001 certification and SOC 2 Type II attestation, owning control design, evidence collection, and auditor engagement end to end — then implemented Vanta for continuous compliance and vendor risk monitoring, while tuning the estate and remediating recurring root causes.

Certified and attested. Monthly security alert volume down 20%, from 110 to 88.

Principal Consultant / vCISO — Independent practice

The security executive for firms that could not hire one

Small law practices and nonprofits carrying real exposure with no in-house security function. I served as their security executive — setting direction, aligning the environment to security and compliance requirements, hardening Microsoft 365 and identity, then pressure-testing it with leadership tabletops and penetration testing.

Four organizations brought into compliance alignment. Exploitability proven rather than assumed, with risk-ranked remediation and retest validation.

Consolidation — NOBULL

Two endpoint stacks collapsed into one

Devices were managed across overlapping tools with no single source of enrollment truth. I retired the redundant MDM and merged the survivors into one co-managed stack — one plane owning enrollment, zero-touch provisioning, compliance policy, and conditional access; the other owning RMM, patching, scripting, and ticketing.

$12K in annual recurring license spend eliminated and machine sprawl ended, with zero end-user downtime.

Automation — NOBULL

Three days of onboarding down to one

Joiners and leavers moved through a manual checklist across half a dozen systems. I automated the path end to end across Microsoft Graph, Slack, the service desk, and serverless edge workers.

Onboarding and offboarding cut from 3 days to 1.

Platform — NOBULL

MCP infrastructure with identity underneath it

I wrote the internal MCP servers that broker agent access to Snowflake, GitHub, Slack, and Azure Container Apps — Entra ID External OAuth, per-role token acquisition via managed identity, a self-healing IT operations agent with a three-tier autonomy model, and an audit evidence layer. It runs on Azure Container Apps, the managed Kubernetes-based platform, with every environment defined as infrastructure as code in Terraform and Bicep, network security groups segmenting it, and CI/CD doing the deploys — secrets held in 1Password and injected at deploy time rather than committed to source. I administer and govern the Snowflake and GitHub organizations those servers reach into.

Delegated agent access that survives an audit. Plus an executive BI command center on Cloudflare Workers with Snowflake as single source of truth.

Cost — Elkus Manfredi Architects

Three hundred thousand out of a $1.7M budget

A decade owning the IT budget and the full vendor portfolio for a 300-person firm. I consolidated overlapping vendors and renegotiated contracts against what the business actually consumed.

$300K in recurring annual savings — 18% of the budget.

Operations — Education Development Center

Five thousand endpoints, a hundred thousand alerts

Security operations and tooling ownership across a 5,000-machine estate for a federally funded research organization, on the Rapid7 platform.

100,000+ alerts triaged annually. Environment hardened to FedRAMP, FISMA, ISO/IEC 27001, SOC 2, and HIPAA control requirements.

Leadership — U.S. Army

Thirty people, five thousand users, three deployments

Led Signal and Cyber Operations teams across domestic bases and three overseas sites, accountable for training, readiness, performance, and career development — while owning the communications and information systems the mission ran on, including the deployed comms Civil Affairs teams operated on for partner-nation and interagency missions.

Zero mission-impacting outages. Training programs cut user-driven incidents 35%.
Roger Figuereo outdoors, leaning against a wooden postRoger Figuereo seated outdoors, laughing

Operating range

Identity & security
Entra ID, Conditional Access, Zscaler ZIA/ZPA, Microsoft Defender XDR, Huntress MDR, CrowdStrike Falcon, Cloudflare WAF and Zero Trust, Rapid7, Microsoft Purview, Metasploit.
Governance & compliance
ISO/IEC 27001, SOC 2 Type II, NIST CSF 2.0, CIS Controls, FedRAMP, FISMA, HIPAA, NIST AI RMF 1.0, ISO/IEC 42001. Vanta. Policy authorship, control design, evidence collection, auditor engagement, third-party risk.
Cloud & data
Azure (primary) — Container Apps, Terraform and Bicep, managed identity, network security groups and segmentation. Snowflake and GitHub (organization administration and access governance), Cloudflare Workers, AWS (supporting — IAM, backup targets).
AI & automation
Multi-platform enterprise AI administration — Claude, ChatGPT, Microsoft Copilot, Perplexity. MCP server development, infrastructure as code on Azure (Terraform and Bicep), CI/CD build and deploy pipelines, secrets management in 1Password injected into Git workflows and Azure Container CLI deploys, TypeScript, PowerShell, Microsoft Graph API.
Endpoint & continuity
Microsoft Intune, NinjaOne, Intune + NinjaOne co-management, Autopilot, Windows and macOS fleet management. Commvault, NetApp, Synology NAS.
Platforms
Microsoft 365, Freshservice, Shopify, Snowflake, Slack, Asana, Tableau. Cisco Meraki firewall, SD-WAN, switching, wireless.

Track record

  1. 2025 — PresentCurrent

    Senior Systems & Security Administrator

    NOBULL — Boston, MA

    Senior IT and security owner for a ~200-employee national DTC athletic brand. One direct report, a $1.1M+ annual technology budget across 15 vendor contracts, and the full security and AI governance stack: identity and access, zero-trust network access, endpoint detection and managed response, unified endpoint management, edge protection, and enterprise backup and recovery.

    Built from zero

    • The AI governance program — Acceptable Use Policy and MCP Permission Policy over a 17-permission delegated access model — and the four enterprise AI platforms rolled out and administered under it
    • Enterprise backup and disaster recovery across Microsoft 365, AWS, and Google workloads
    • Zero-trust network access, replacing legacy VPN with brokered per-application private access
    • The IT service management function — service desk, ITIL workflows, and measured SLAs
    • The internal MCP servers — written in house, running on Azure Container Apps and deployed as infrastructure as code — brokering agent access to Snowflake, GitHub, and Slack under Entra ID External OAuth with an audit evidence layer
    • The third-party security review pipeline gating every platform before procurement

    Consolidated two overlapping endpoint management stacks into one co-managed platform, cutting $12K in annual license spend with zero end-user downtime.

  2. 2023 — 2025

    Principal Consultant / vCISO

    Independent IT & Cybersecurity Consulting — Greater Boston

    Ran concurrent with the Education Development Center role from June 2024.

    Acting security executive for four clients — small law practices and nonprofits with no in-house security function. Built greenfield environments from zero, set security direction, brought each into alignment with security and compliance requirements, and ran leadership tabletops and penetration testing with Metasploit.

  3. 2024 — 2025

    Information Security Analyst III

    Education Development Center — Waltham, MA

    Security operations and tooling ownership across a 5,000-machine estate for a federally funded research organization. Triaged 100,000+ alerts annually on the Rapid7 platform and hardened the environment to FedRAMP, FISMA, ISO/IEC 27001, SOC 2, and HIPAA control requirements.

  4. 2013 — 2023

    IT Manager

    Elkus Manfredi Architects — Boston, MA

    IT and security function owner for a 300-person architecture and design firm: three direct reports all hired and developed in seat, MSP partner oversight, the full vendor portfolio, and a $1.7M annual budget. Delivered $300K in recurring annual savings and led the firm to ISO/IEC 27001 certification and SOC 2 Type II attestation, implementing Vanta for continuous compliance monitoring.

  5. 2010 — 2019

    Lead Security Analyst & Signal Operations Leader

    United States Army — Active Duty & Reserve

    Reserve service ran concurrent with the civilian role.

    Led approximately 30 personnel across Signal and Cyber Operations, including three combat deployments, supporting 5,000+ users across domestic bases and three overseas sites — and delivered the communications Civil Affairs teams operated on for partner-nation and interagency missions. Zero mission-impacting outages; training programs cut user-driven incidents 35%.
Education & credentials

Education & training
U.S. Army Signal (25-series) and Cyber Operations (17-series) technical training — communications systems, network operations, and cyber defense
Security
CISSP — Certified Information Systems Security Professional · CompTIA Security+ · OWASP SAMM Fundamentals
AI & cloud
Claude Certified Architect · Microsoft Certified: Azure AI Engineer Associate · AWS Certified AI Practitioner · Google Cloud Professional Machine Learning Engineer
Clearance
Previously held a U.S. government security clearance during Army service — favorably adjudicated, U.S. citizen, eligible for sponsorship and reinvestigation
Service
Army Commendation Medal · Army Achievement Medal (multiple) · National Defense Service Medal · Afghanistan Campaign Medal · Global War on Terrorism Service Medal
Languages
English and Spanish, both native/bilingual

Let's talk about scope

I'm open to director-level technology and security leadership roles in Greater Boston and remote-friendly organizations nationally. The fastest way to reach me is email.